Homelab
My personal infrastructure: virtualisation, network storage, a private network and a Kubernetes cluster built from scratch, hosting my other projects.
- Year
- 2026
- Context
- Personal project, my experimentation ground
- Tech stack
- Proxmox
- Synology
- Networking
- Tailscale
- Docker
- Kubernetes
- Terraform
01 · Context
The challenge
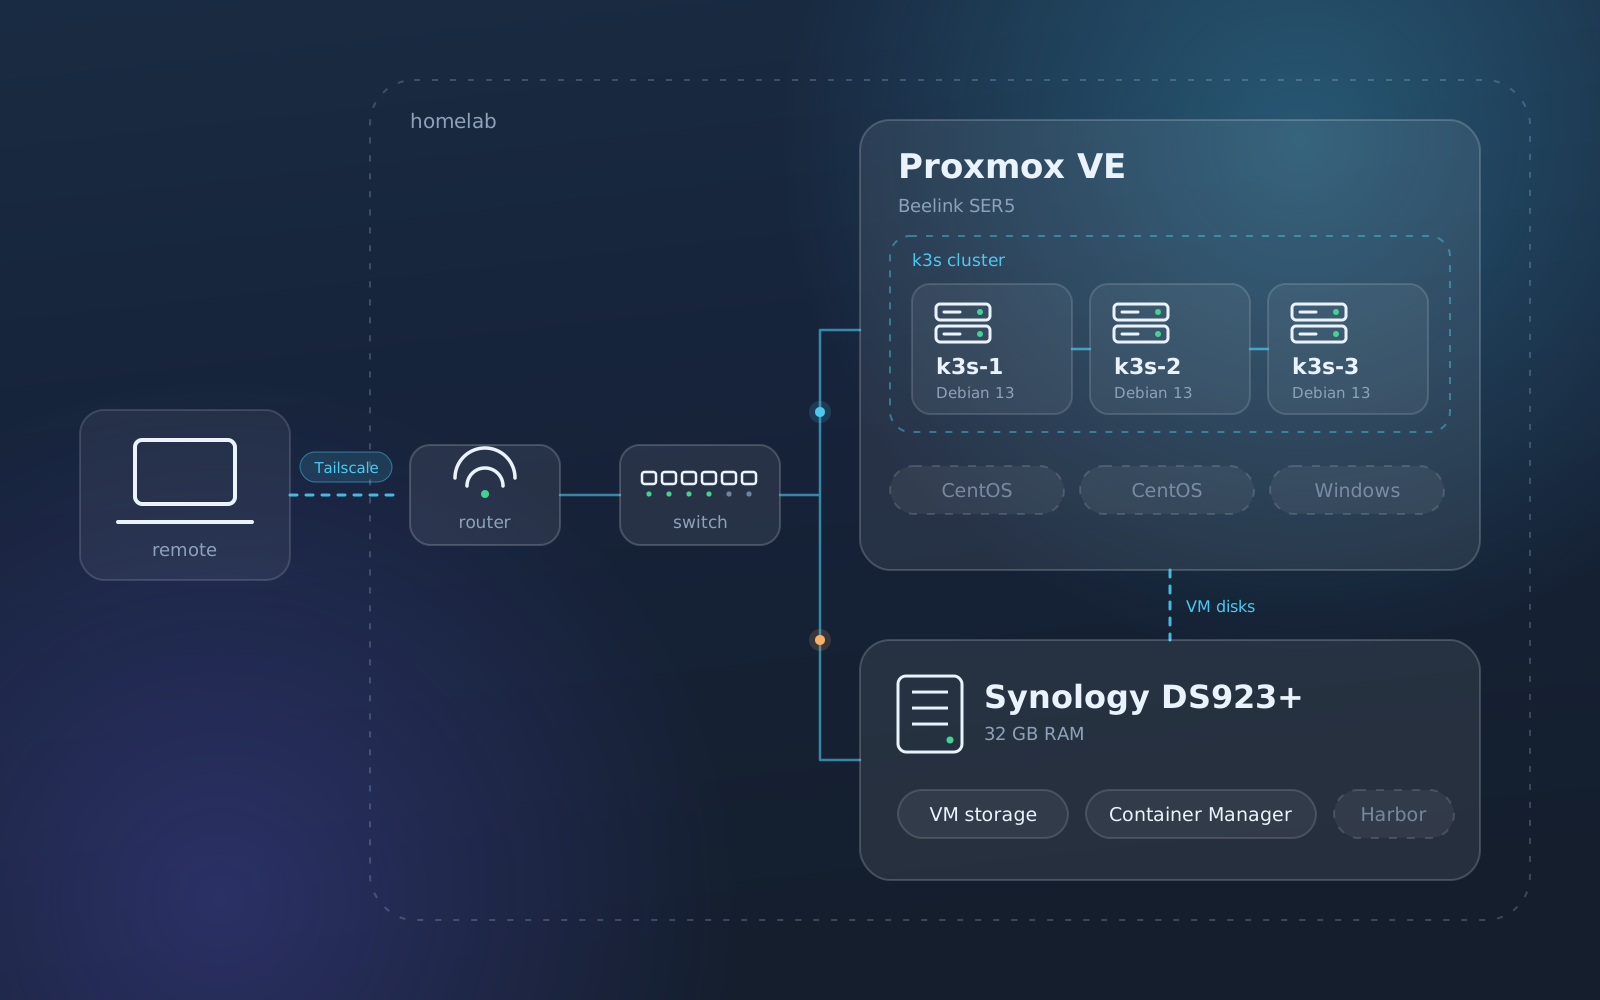
As a tenant in a flat with shared wifi, with no access to the ISP router and no static IP, I built my own private network (a range extender, a small router, switches) on 192.168.2.0/24 to get a real playground for experiments. A mini PC runs the Proxmox hypervisor and its virtual machines; it is often switched off overnight. A Synology NAS acts as storage and container platform, and hosts Verkko, my network scanner, which tracks my static IPs and my VMs. For Opi! I built a k3s cluster of three Debian 13 VMs on it: a Proxmox template cloned by Terraform, then k3s, Traefik, password encryption with Sealed Secrets and the Tailscale operator. The Harbor image registry runs on the NAS and Argo CD deploys the site on every merge. The cluster has no open port, neither to the Internet nor to the local network: it can only be reached through Tailscale, over HTTPS, from my own devices. Opi!'s database is backed up to the NAS every evening, and Prometheus watches the backup. A second private network is planned.
02 · Architecture
How it's built
Key points
- Proxmox hypervisor on a Ryzen 7 / 32 GB mini PC, and a Synology DS923+ NAS for storage and containers
- Dedicated private network (router, switches, range extender) on 192.168.2.0/24
- Remote access through Tailscale, with no open port to the Internet
- k3s cluster of three Debian 13 VMs, created with Terraform from a Proxmox template
- Private image registry (Harbor) on the NAS, and continuous deployment by Argo CD
- Passwords encrypted before they enter Git, with Sealed Secrets
- Nightly backup of Opi!'s database to the NAS, and monitoring with Prometheus
- Verkko, a home-made network scanner, to track static IPs and VMs
03 · In pictures
Gallery
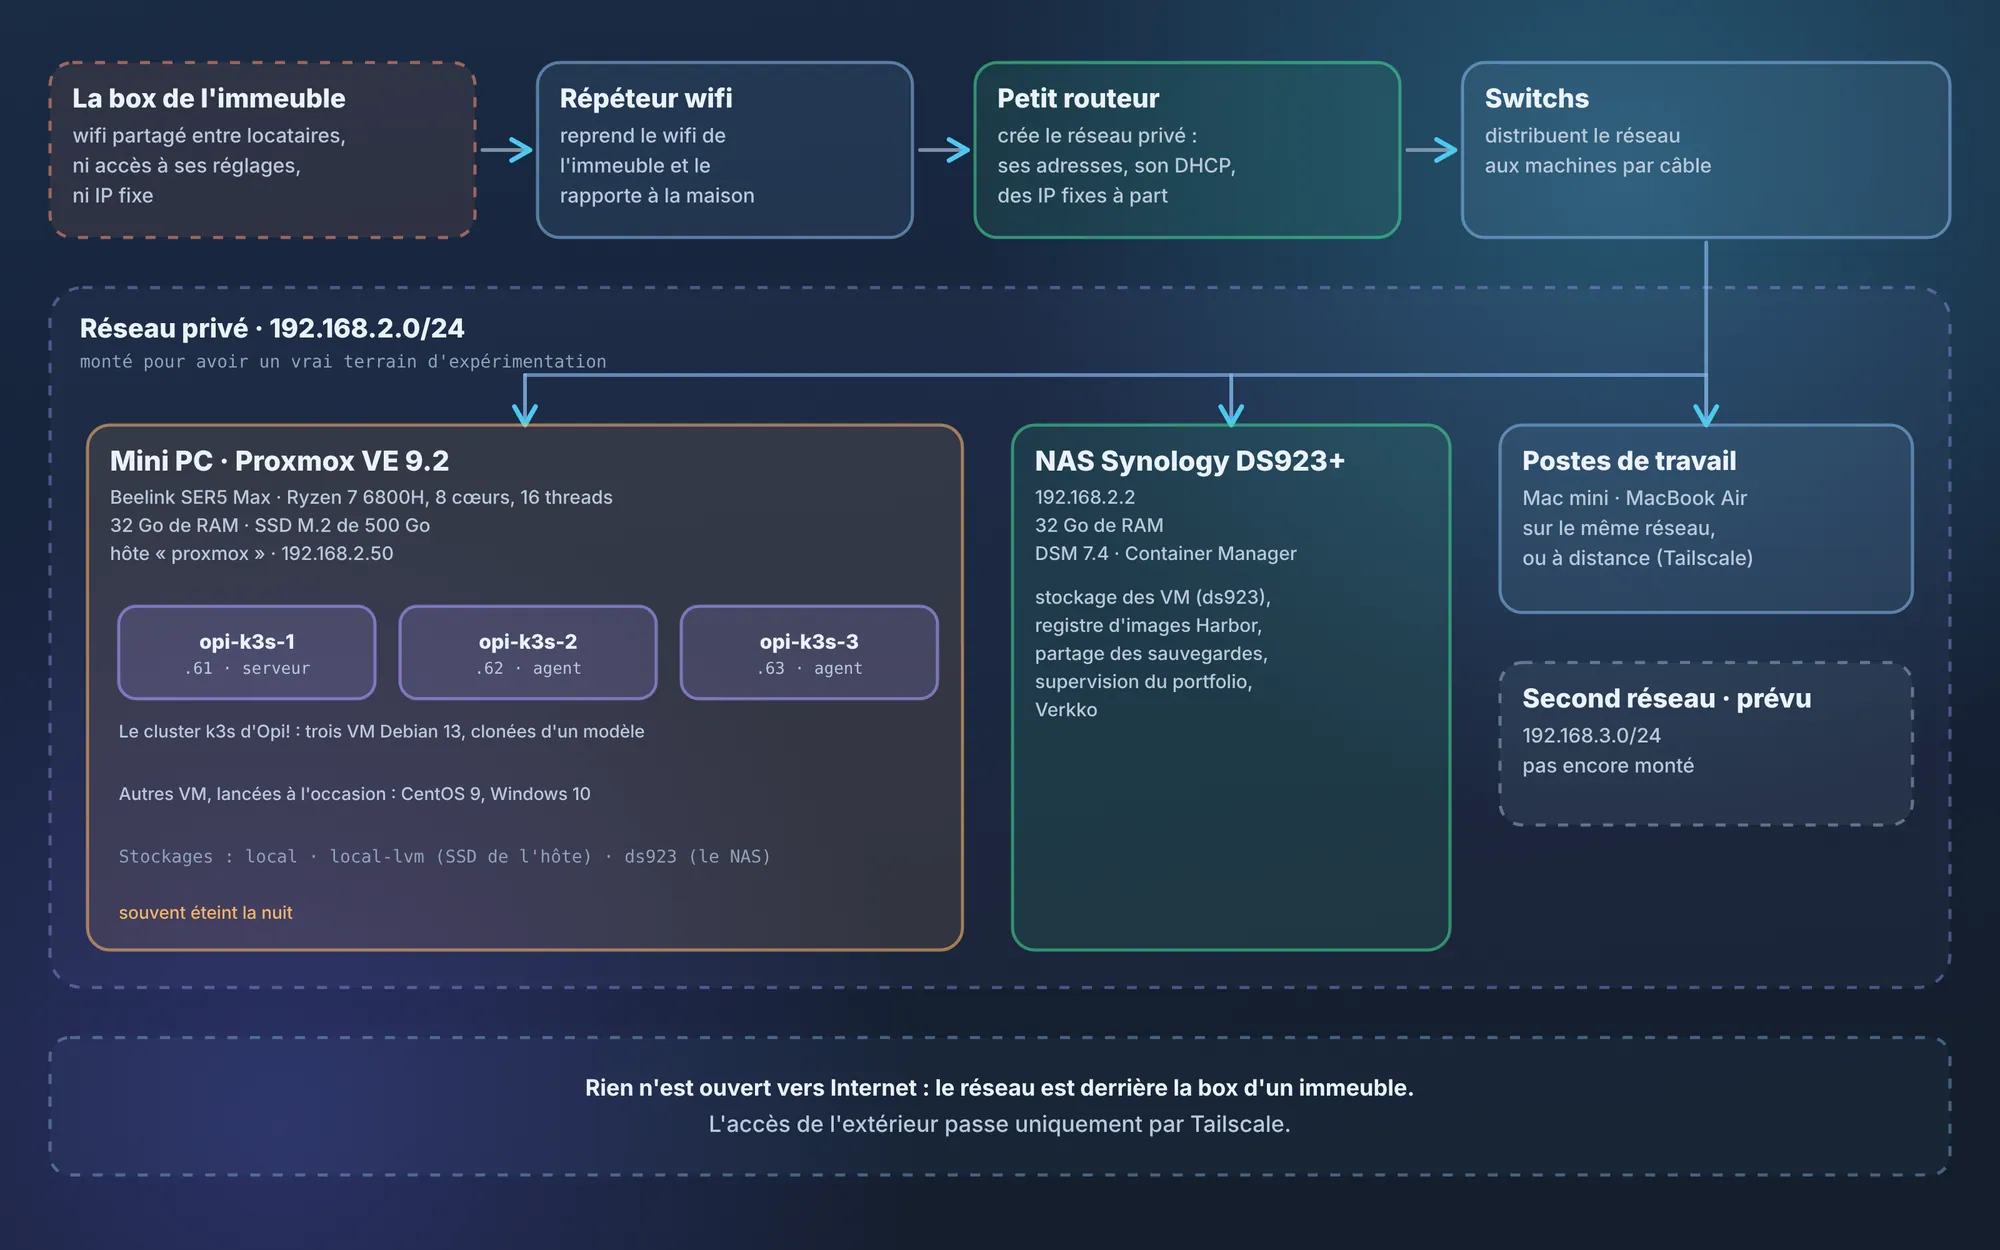
Hardware and network: the building's router, the private network built behind it, the mini PC, the NAS and the workstations 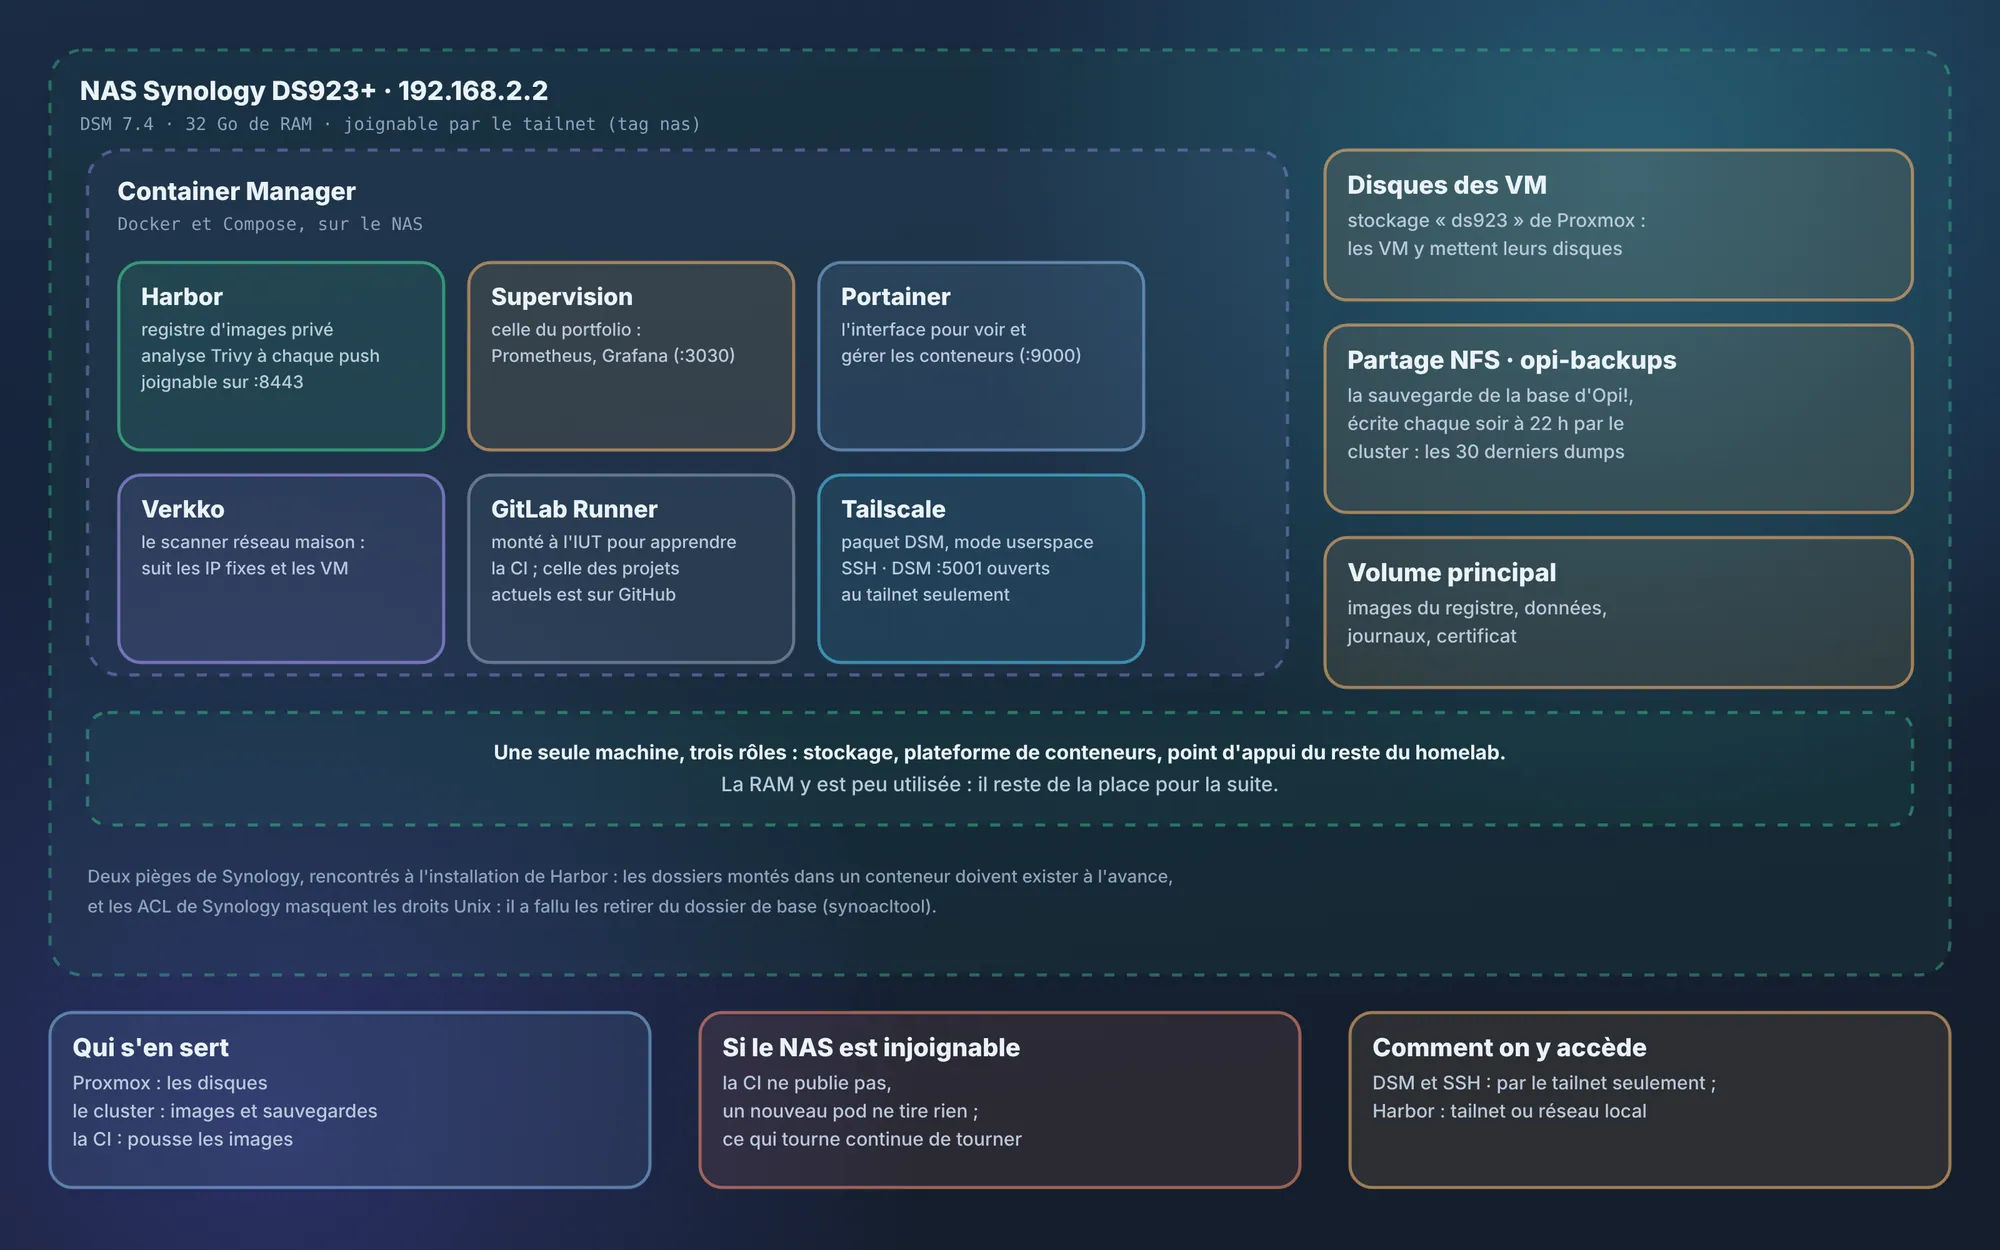
The NAS: storage, image registry, monitoring and containers on a single machine 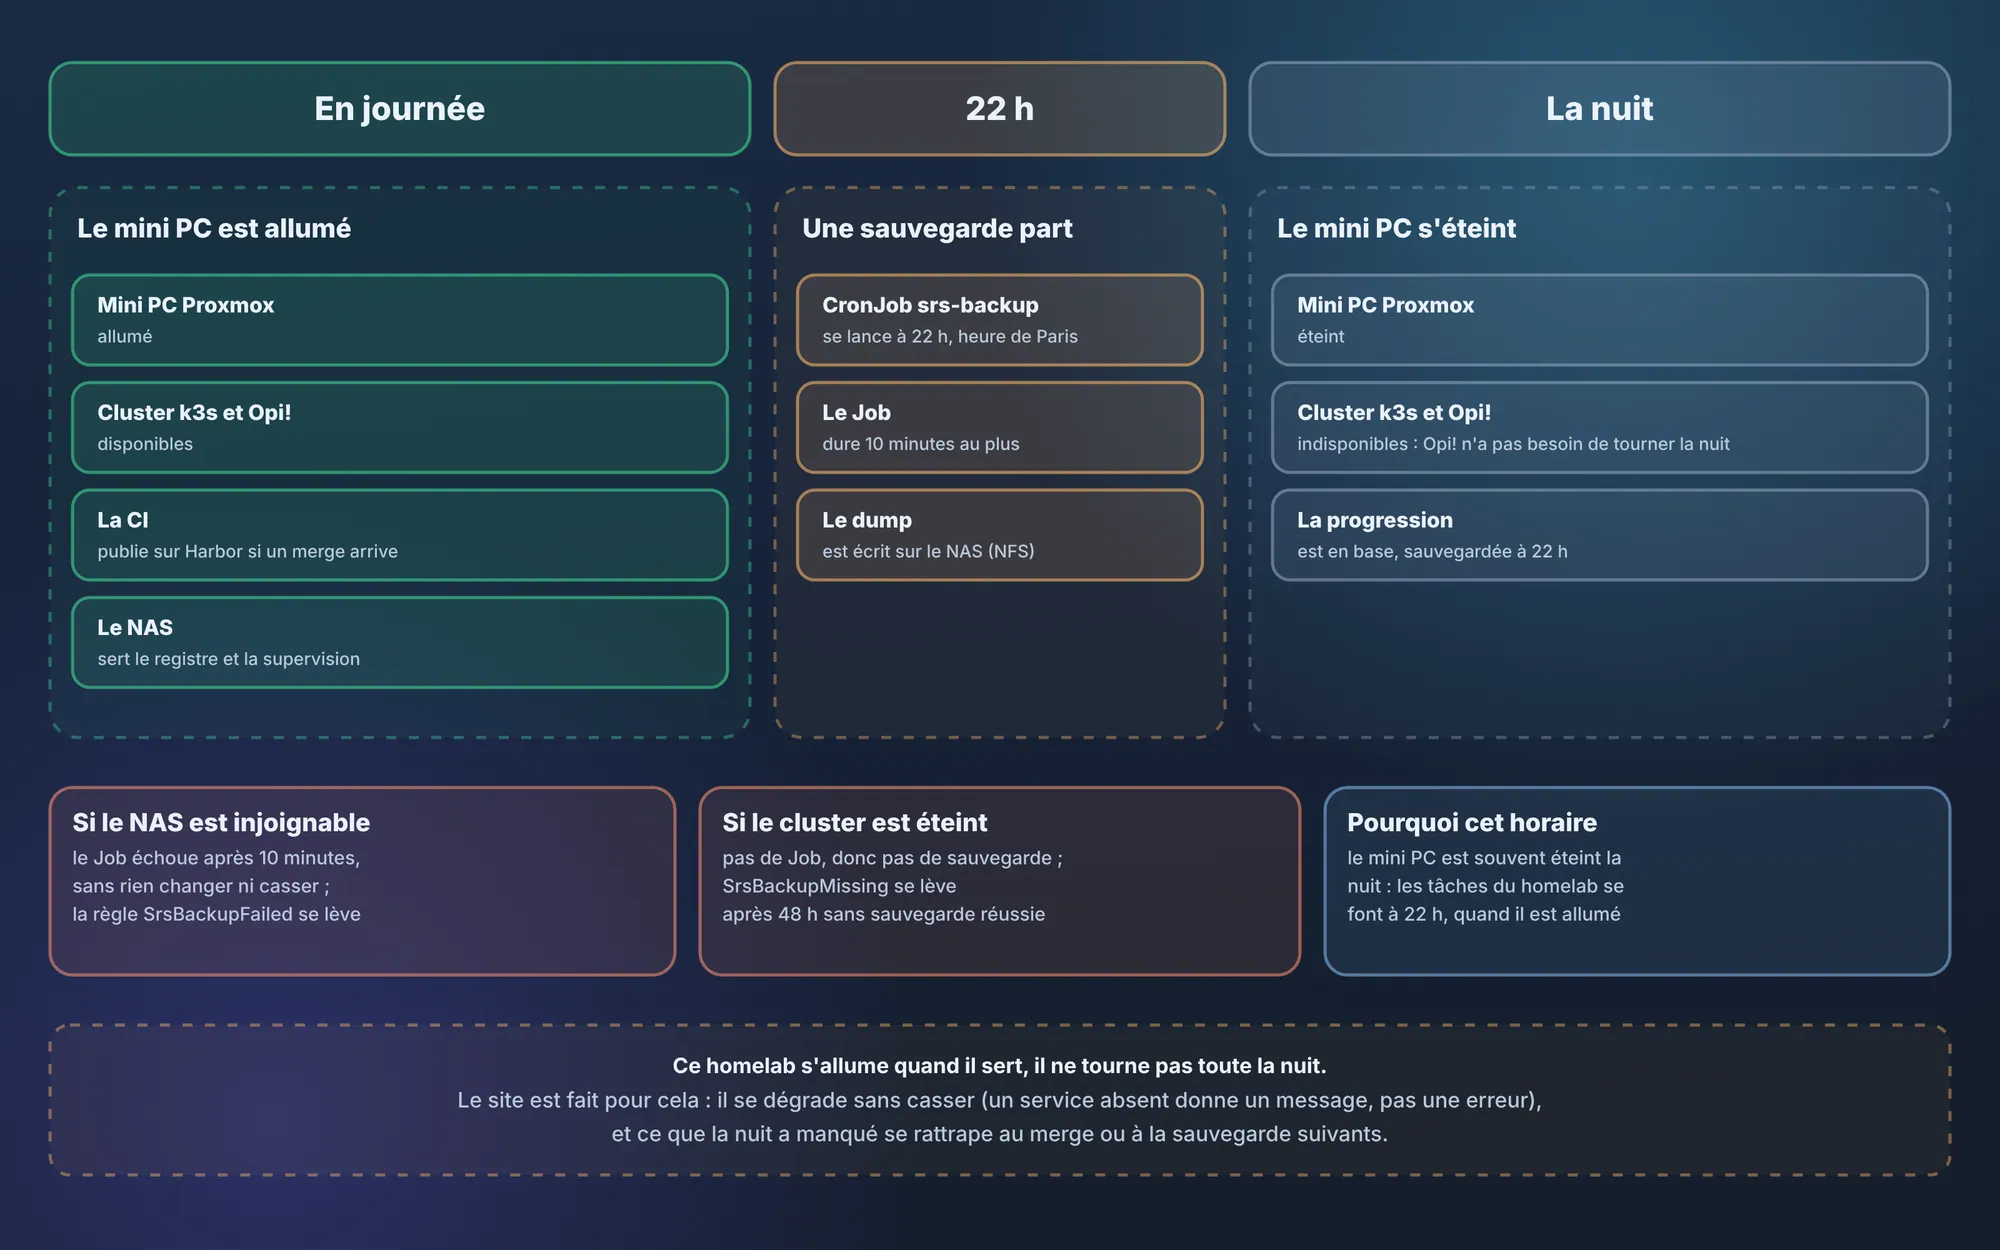
A day in the homelab: the mini PC on by day, a backup at 10 pm, off at night 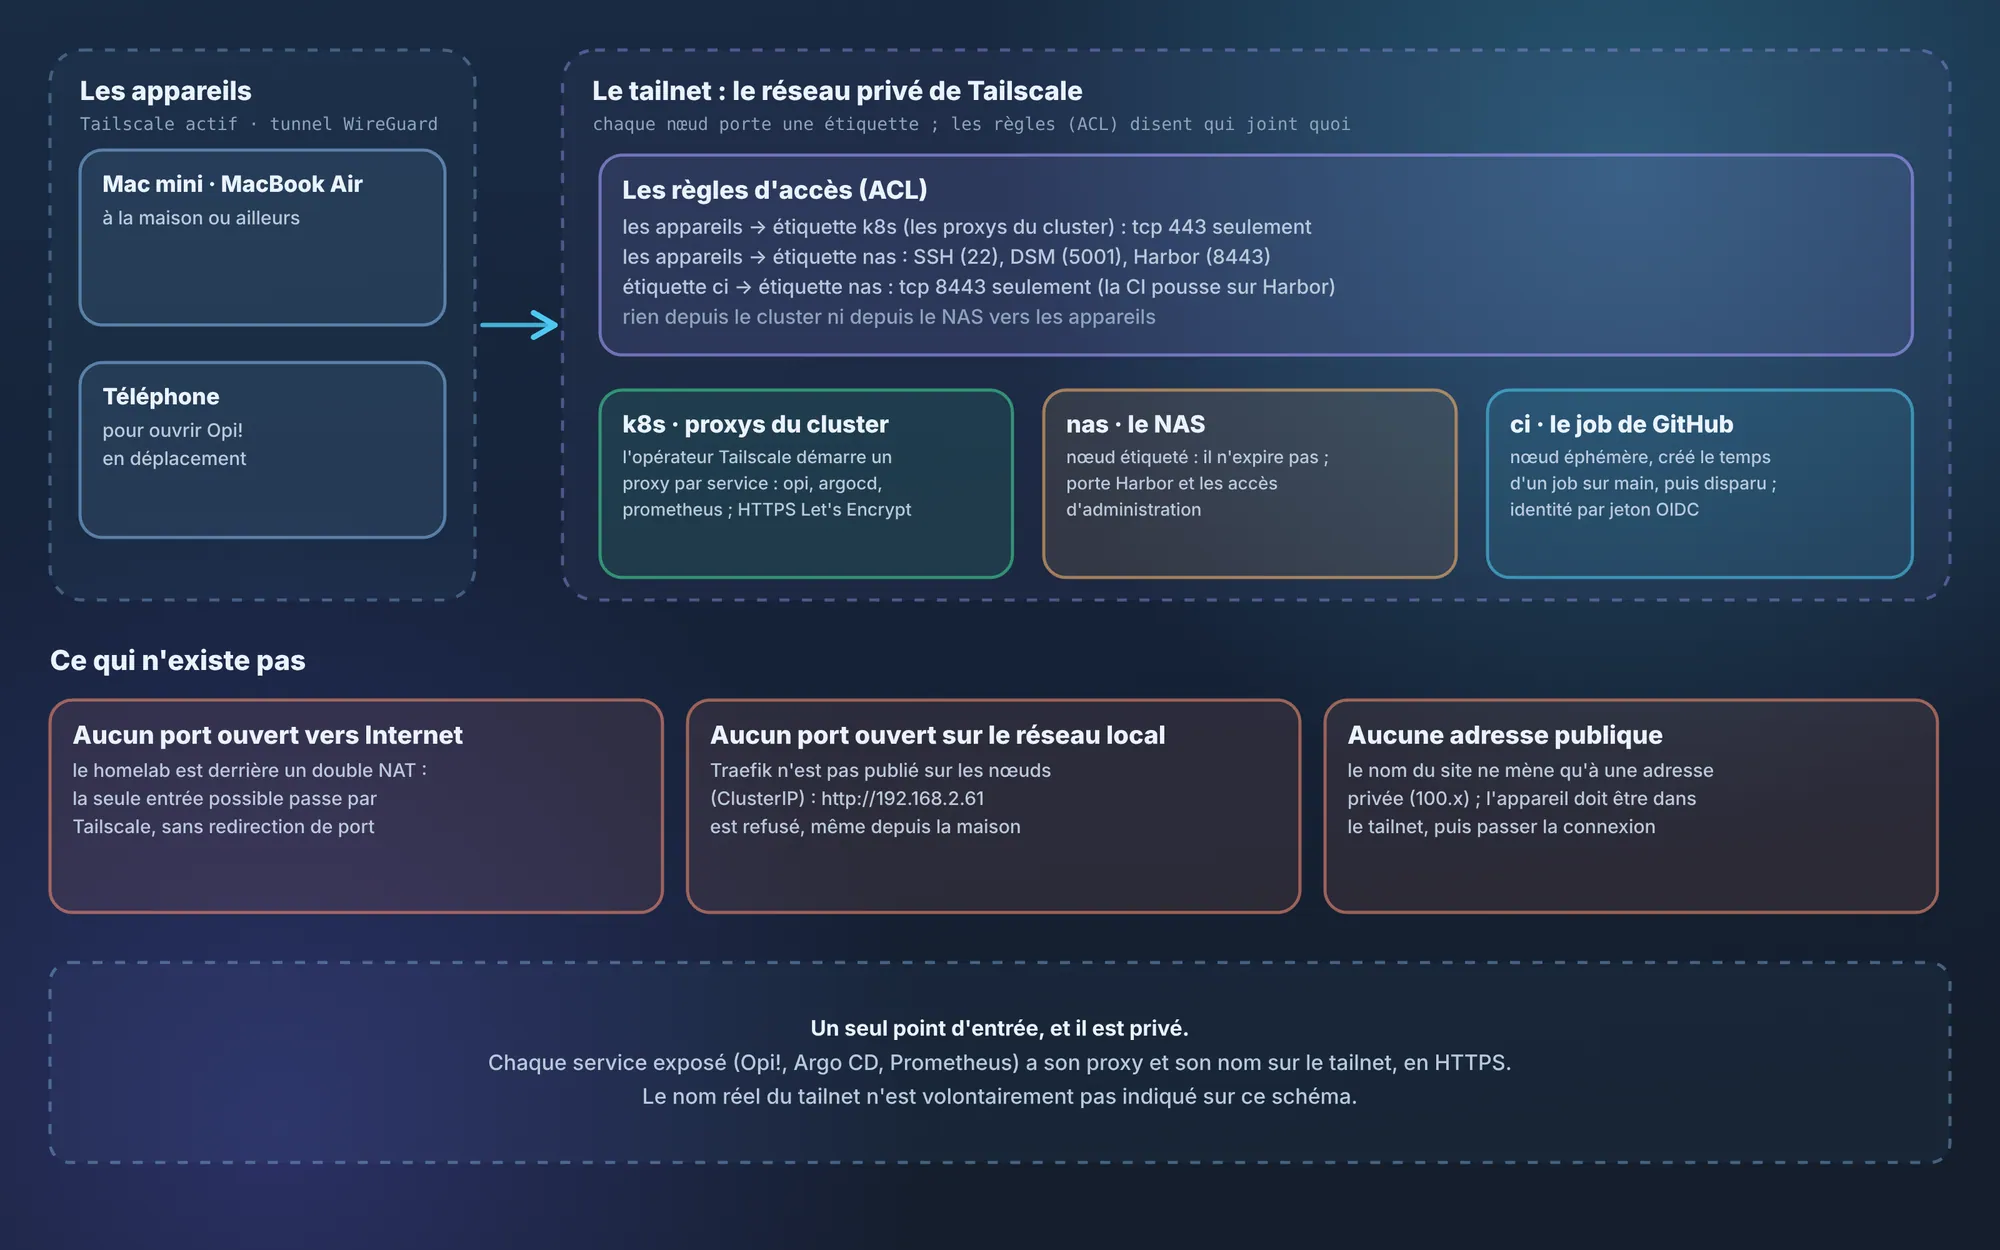
Remote access: the tailnet, its rules and what is not exposed 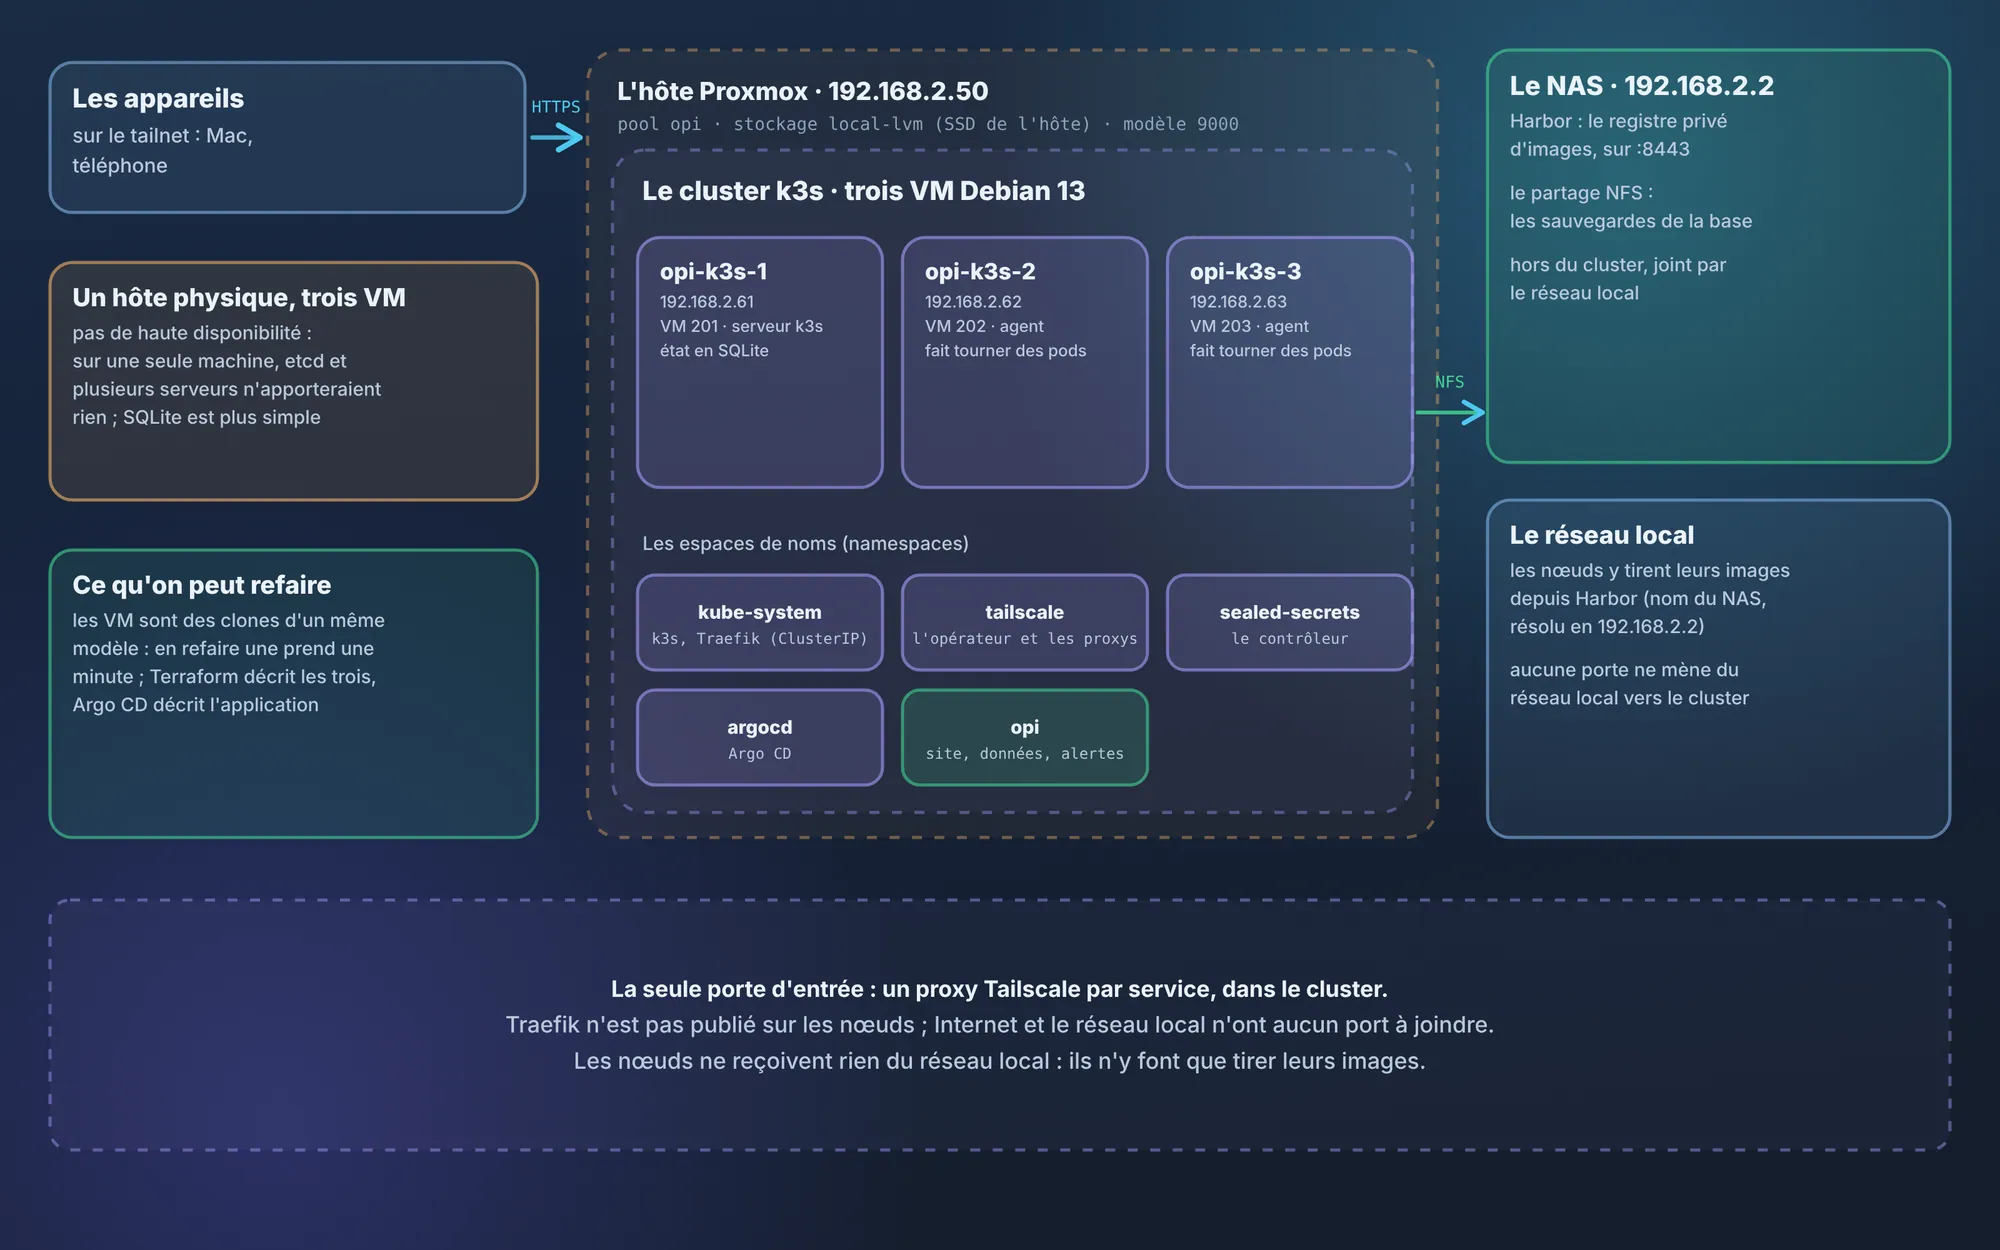
Overview of the cluster, from the Proxmox host to the namespaces, and its only entrance 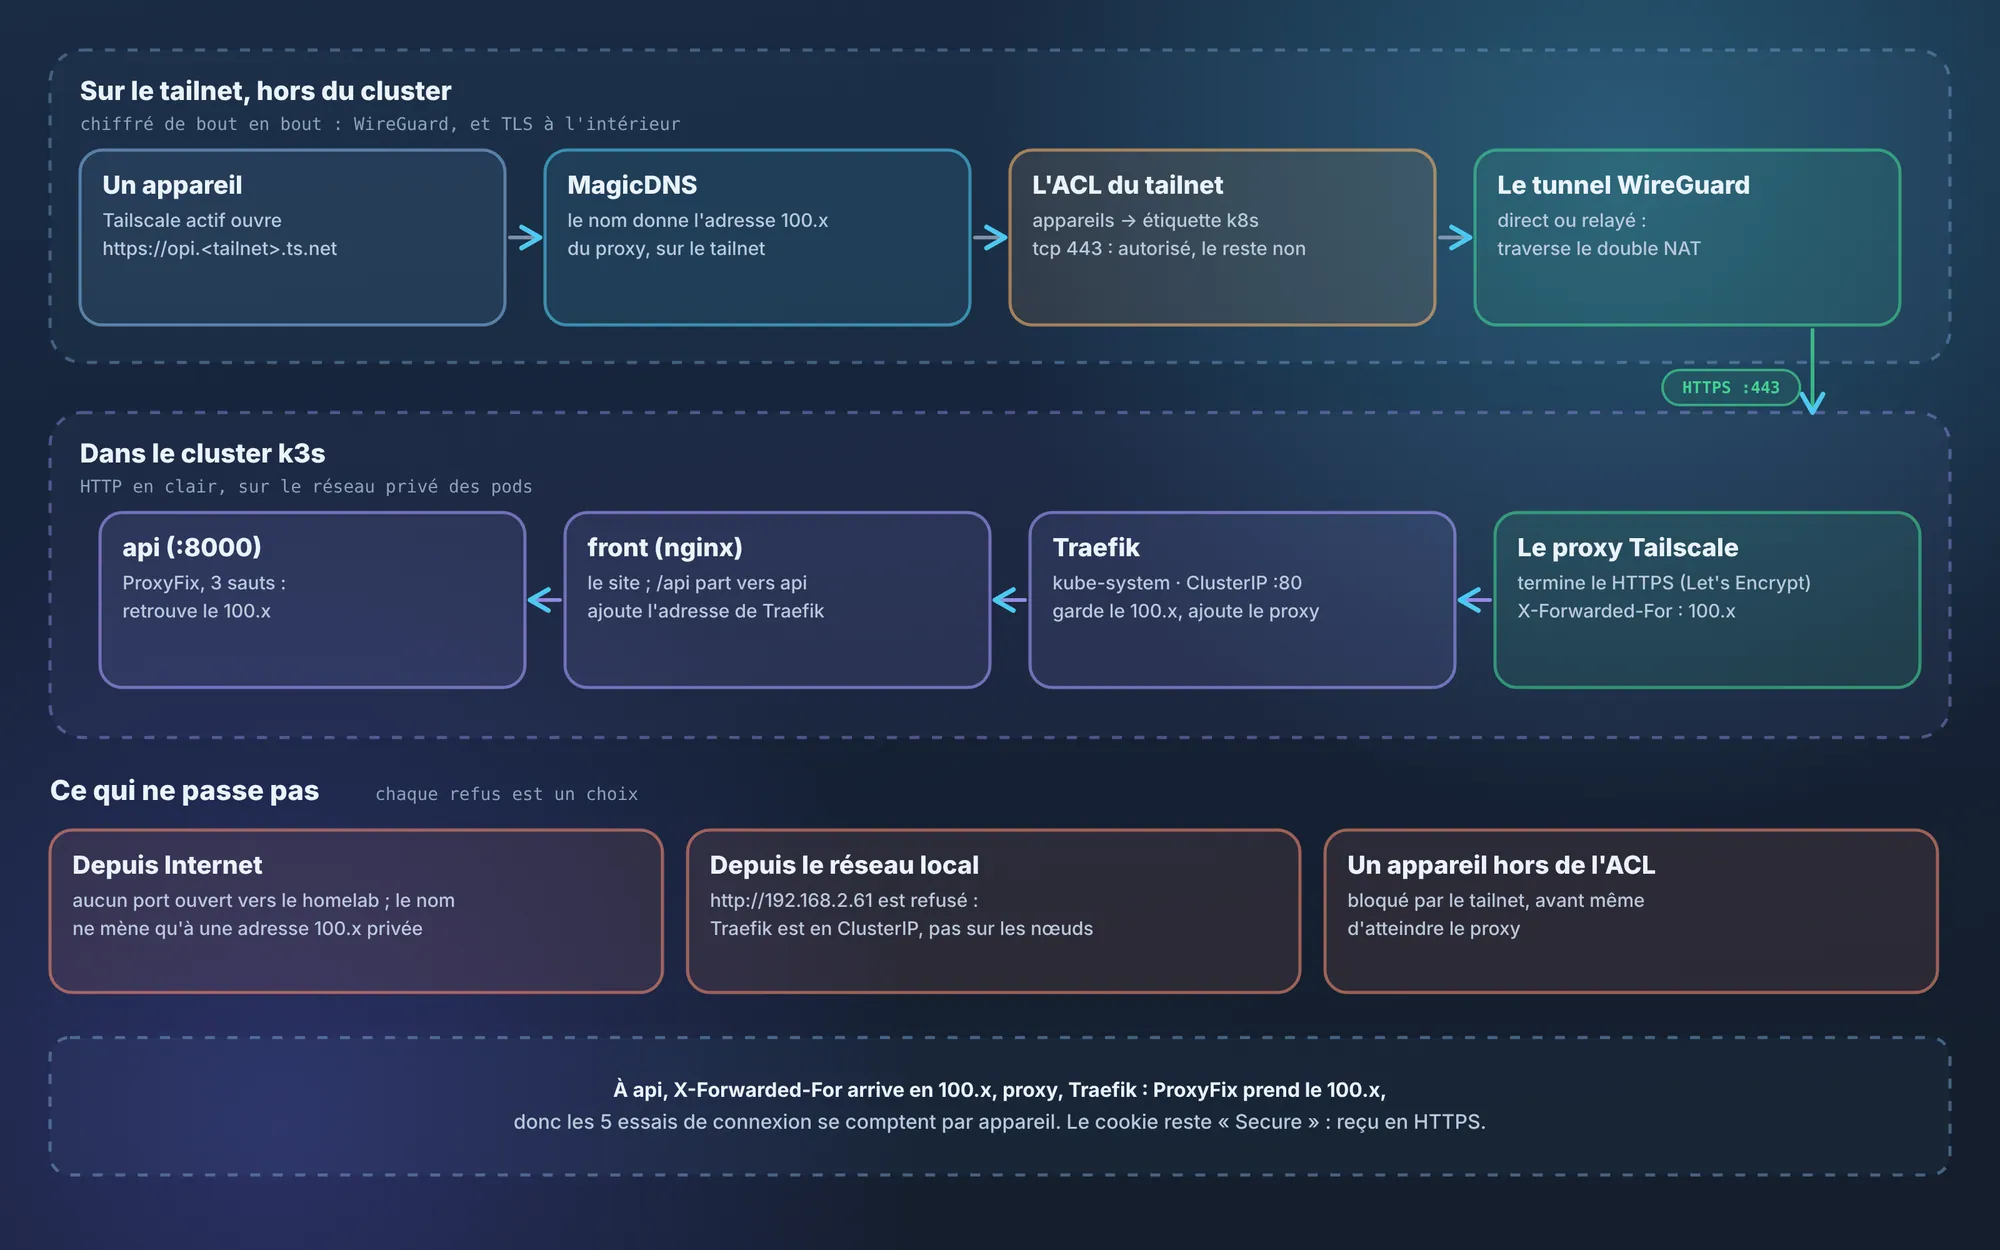
The path of a request, from the device to the pod, and what does not get through 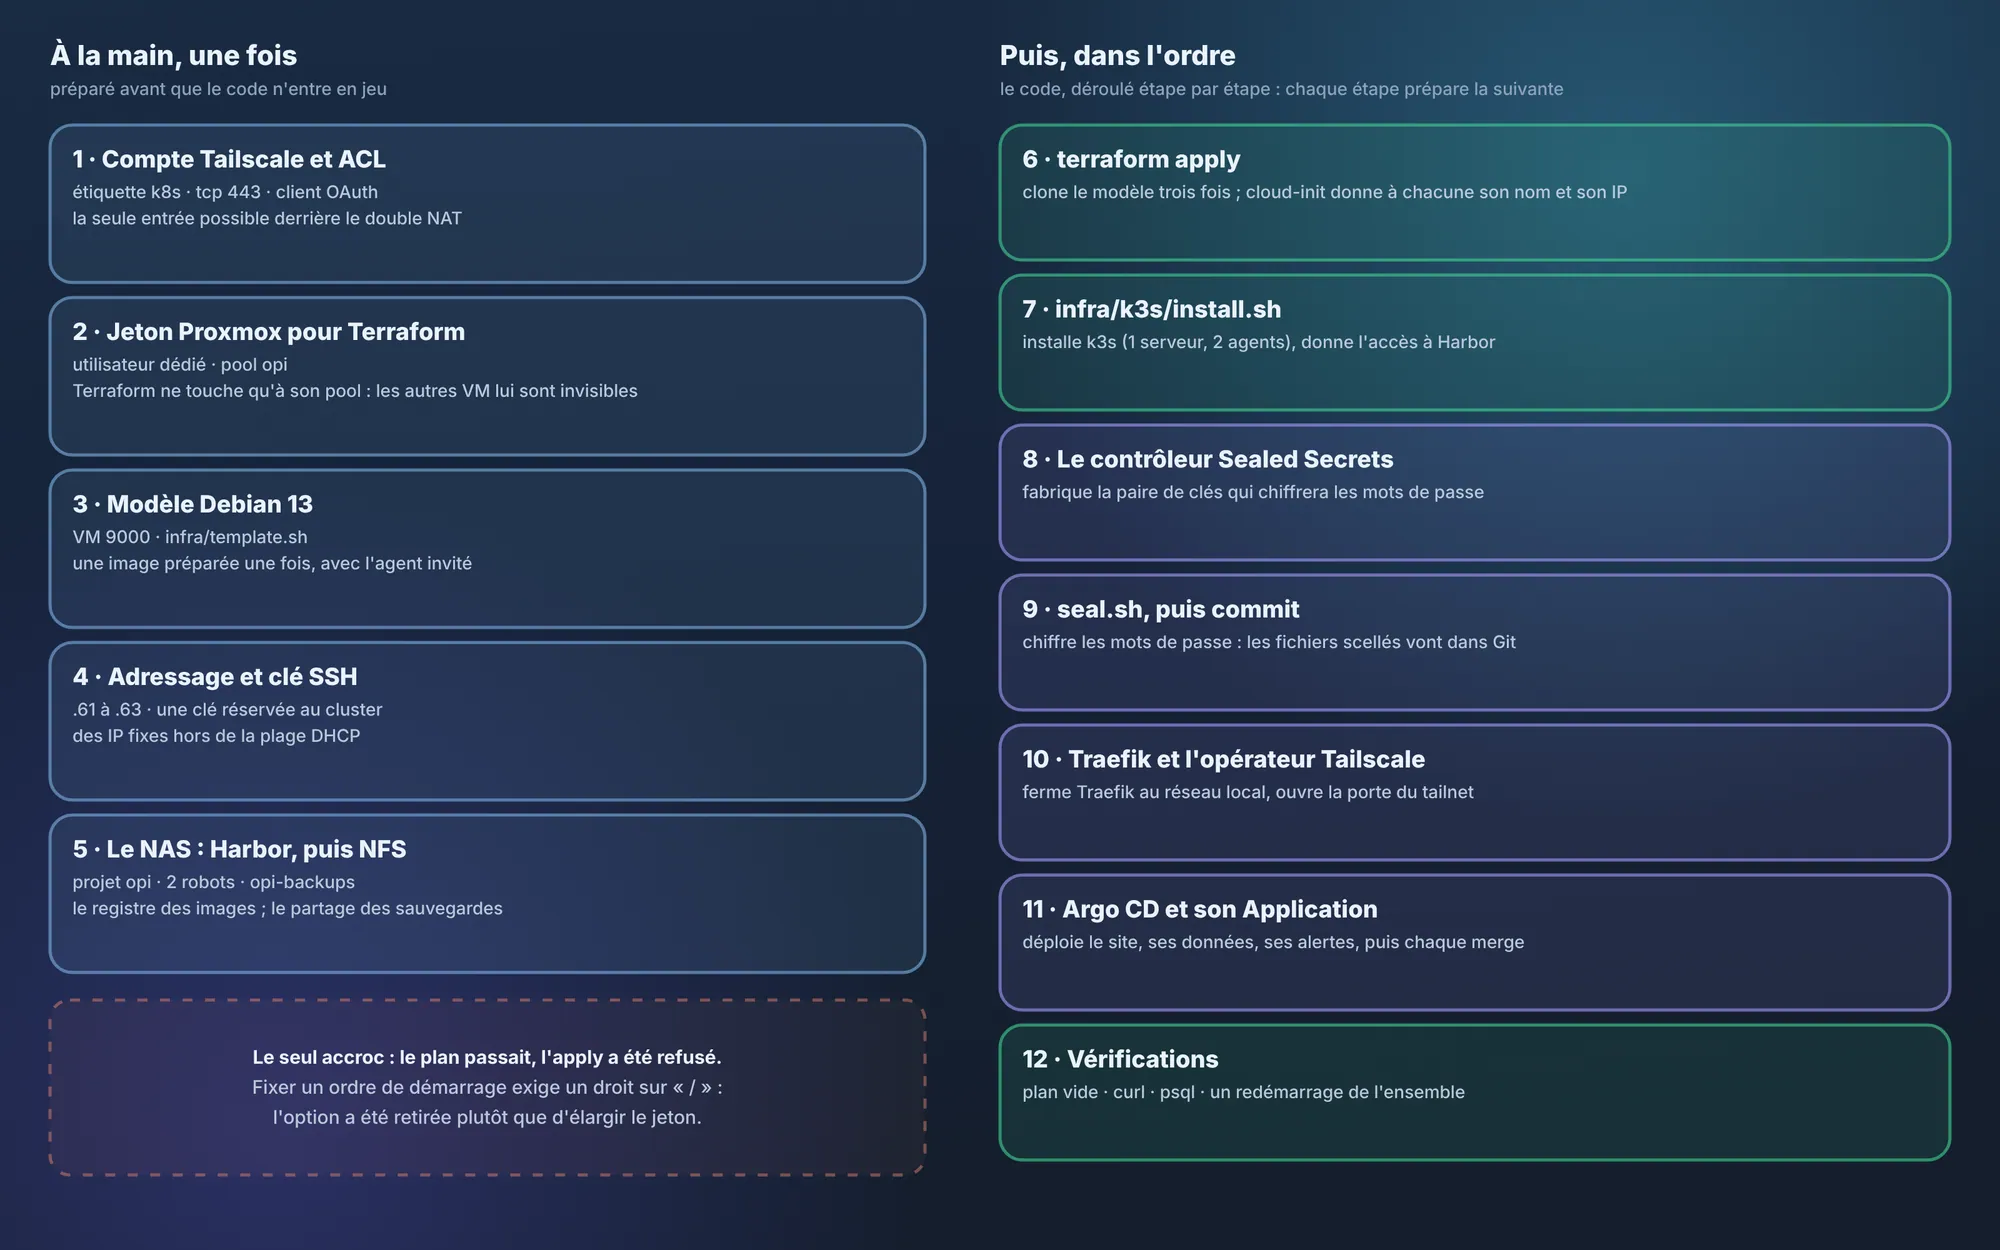
The build order: what was prepared by hand, then carried out step by step 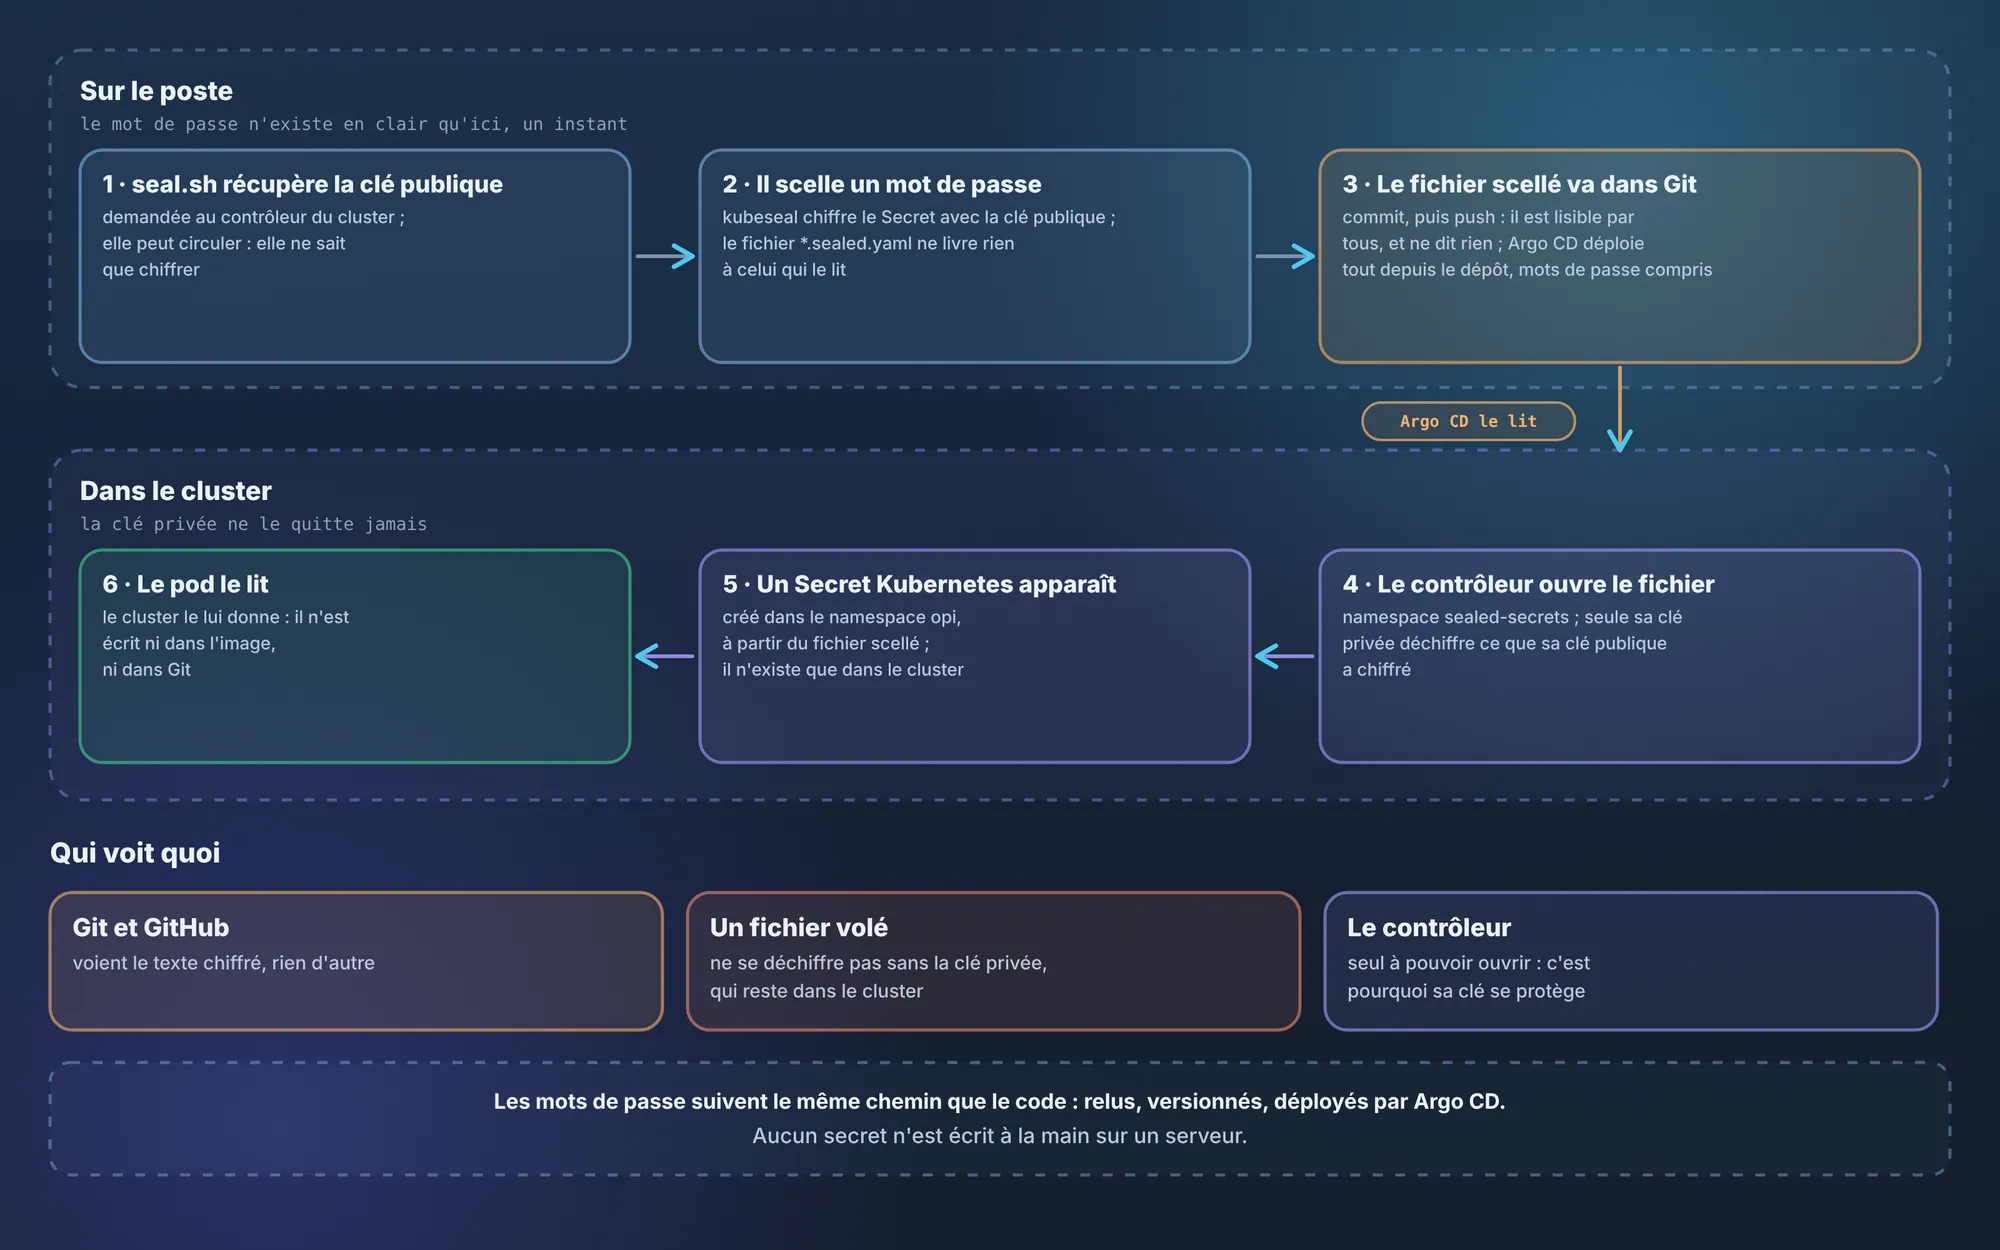
Sealed Secrets: a password goes from the workstation to the pod without ever being readable in Git 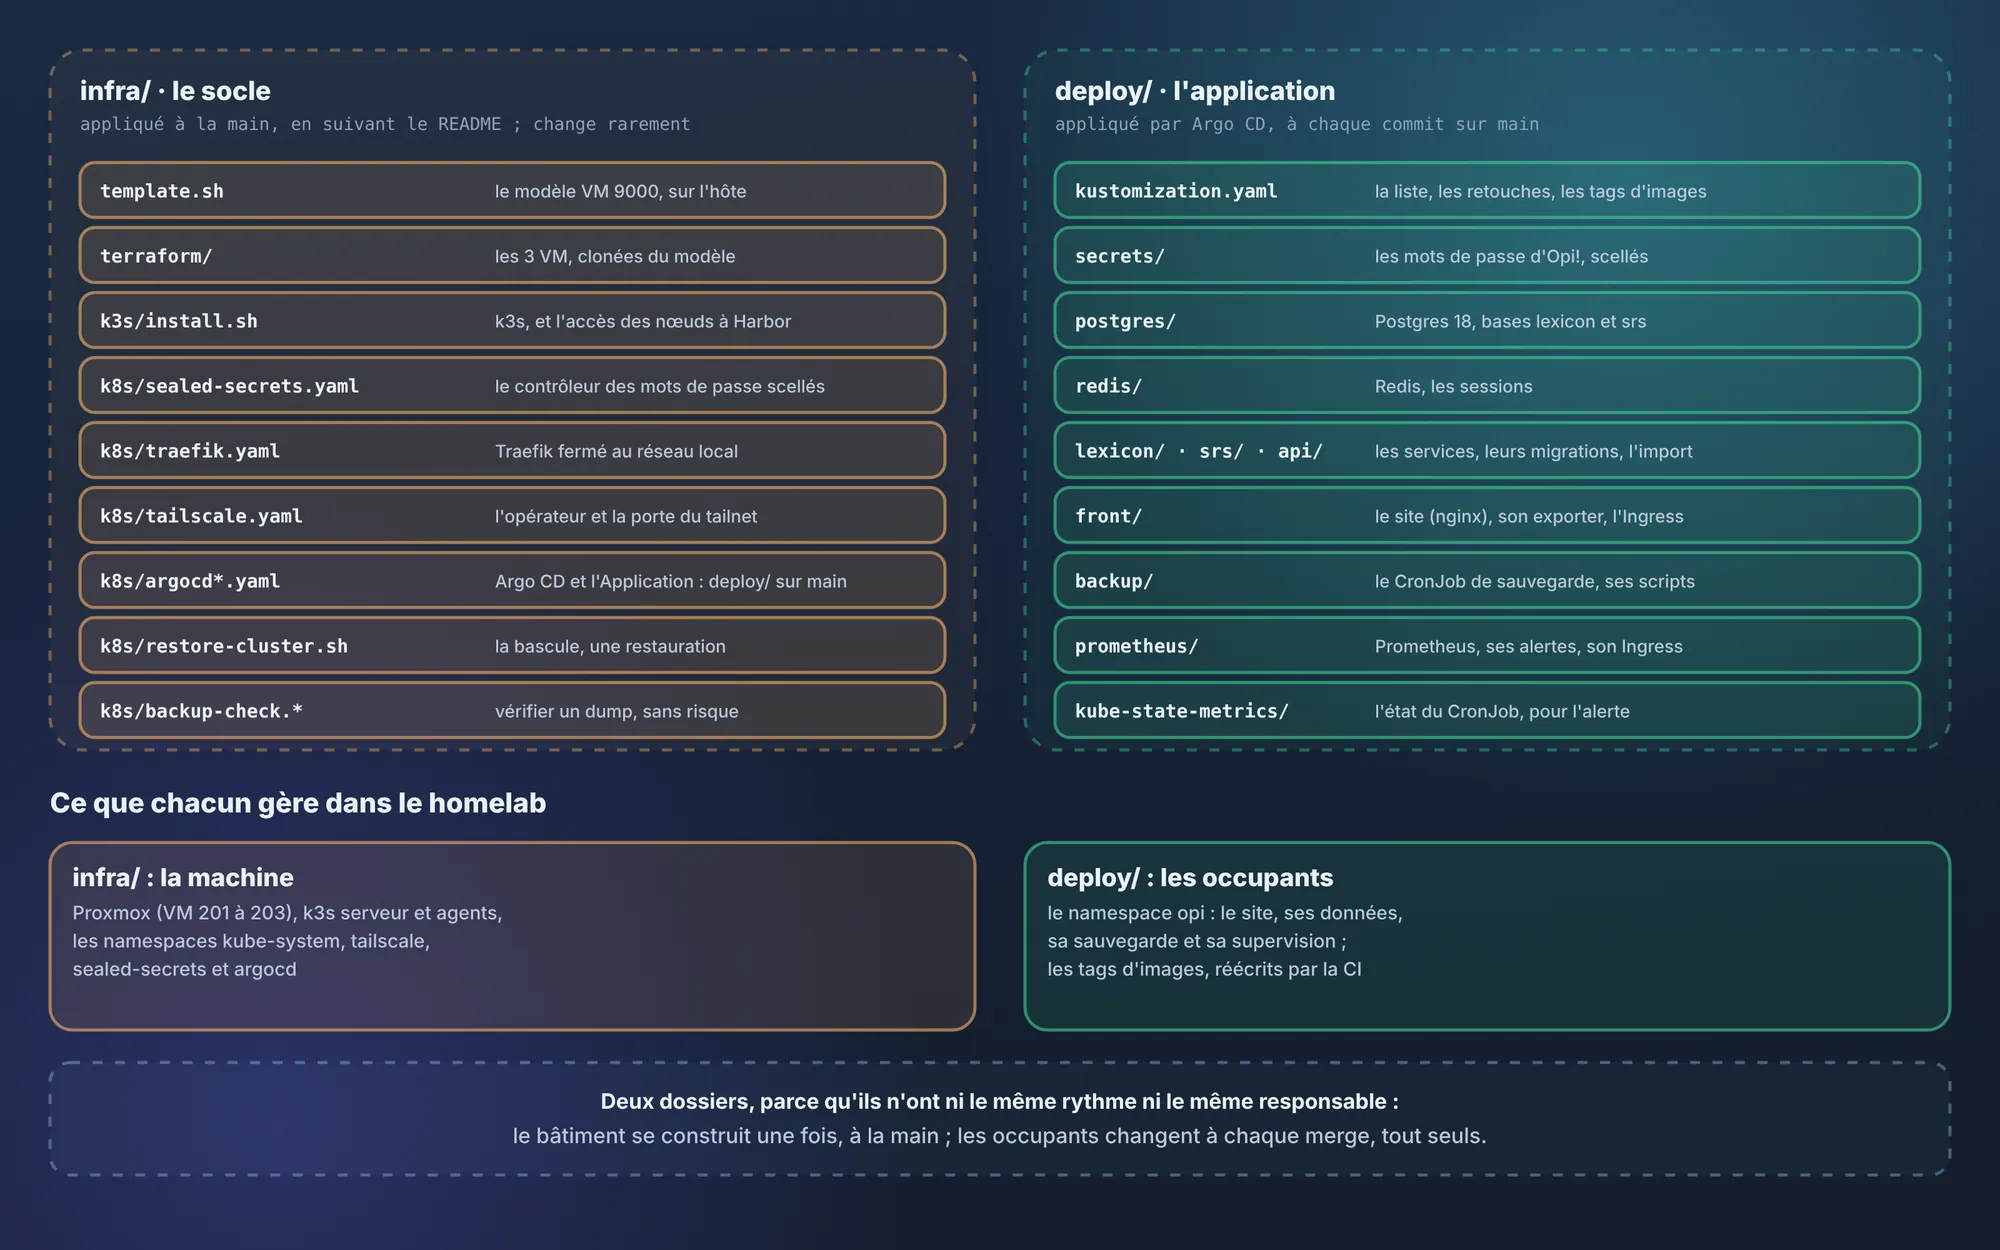
infra/ and deploy/: the foundations on one side, the application on the other
Click an image to open it full screen and browse through the screenshots.
04 · Takeaways
What I took away from it
I learned to build an infrastructure from scratch: a private network behind an ISP router I do not control, a hypervisor, then a Kubernetes cluster created with Terraform. I came to understand in practice what exposing nothing means: a single entry point, through Tailscale, and passwords encrypted before they enter Git.